*update - CMMC v2.0 was introduced on 11/4/2021...additional updates to this article will be included soon.
*update - CMMC v2.0 was published in the Federal Register on 9/10/2025 with 11/10/2025 as an effective date, requiring Phase 1 of a phased rollout, requiring self-assessments for levels 1 and 2. For level 2, in some cases, a self-assessment may not be allowed. Phase 2 of the rollout begins on 11/10/2026 and requires level 2 third-party assessments. Full implementation of CMMC for all contracts will be mandatory on 10/31/2028.
Subscribe to our YouTube CMMC Playlist. CMMC Foundational training is also available from Arrakis at this link.
Contact Arrakis for CMMC support at sales(@)arrakisconsulting.com; however, in the meantime, keep reading and learn a little bit about CMMC below. Arrakis is a CMMC-AB Registered Practitioner Organization (RPO) and a certified CMMC trainer through PECB. Arrakis is also CMMC Level 2 certified.
What is CMMC? If you haven’t heard of CMMC (Cybersecurity Maturity Model Certification) yet, you soon will if you are involved in any capacity on a US Government Department of Defense (DoD) project. CMMCv1 is a five-tiered cybersecurity model in which each tier involves greater maturity and additional requirements. With CMMCv2, the 5-tier model was reduced to 3 tiers. Additionally, each tier builds on the previous tier: to be recognized as mature at level 2 (ML2), you must also do everything required at level 1 (ML1). Currently, only ML1 through 3 have been defined in terms of requirements, with 4 and 5 required for the most secure and sensitive environments…regardless, ML4 and 5 remain unknown. In CMMCv2, tiers 2 and 4 were removed, leaving only tiers 1, 3, and 5 from the original version 1. Most of the original CMMCv1 remains in v2, but with some different structuring. From Arrakis' standpoint, there really isn't any reduction in security with version 2.
Quick video on CMMC for defense contractors
Why we have CMMC is probably obvious to everyone, or at least will be, after reading this paragraph. There are entities hostile to the US Government and the American way of life. These entities could include local US entities, domestic activists, foreign activists, foreign governments, terrorist organizations, disgruntled citizens, or any other entity or person hostile to the US Government. Additionally, some countries (e.g., China) have a strong desire to compromise as many companies as possible to acquire technology without spending on R&D… essentially stealing technology at the expense of the USA and USA-based companies. To cover all our bases for this collection of hostile entities, we’ll call these entities the threat in a very broad sense. It is the DoD's view that the threat may not only attempt to compromise a large prime contractor directly but is more likely to leapfrog through subcontractors to glean just a smidge of data that can later be compiled to produce more sensitive information. This technique is called “island hopping”.
Because of the previous paragraph and the clear examples published in the news over the last two decades, the DoD has determined that something like the CMMC is needed to help protect the USA's security and degrade the threat's technological advancements. Just Google “industrial espionage” and “China” and you’ll see plenty of examples.
CMMC is fairly straightforward in that it is a pass/fail environment, meaning that if you did 99% of it perfectly, then you have failed. Simple. You are either 100% compliant with the CMMC published minimum standards at your desired maturity level, or you are not. Certainly, you can do more than CMMC requires, but some companies will likely find just meeting the standard a challenge in and of itself.
Now, is there flexibility? Yes, there is, but not much, and certainly far less than other regulatory environments. Should an audit team visit you as a part of a company’s certification process, and they discover a “finding”, you do have some ability to remediate that finding and still pass. For example, if you couldn’t prove visitors had signed in when the audit team was there (maybe the person with the sign-in book was sick that day, and it was in a locked file cabinet), then you would have a finding that the audit team could then review later, over Zoom. The finding could then be resolved, and the company would still be eligible for certification. Please also keep in mind that the audit team would likely ask why there was no backup plan in that particular case, or whether visitors were simply not allowed to visit that day. Always remember that every excuse you provide to an audit team, whether CMMC-related or not, is likely to raise additional questions.
Where there isn’t flexibility is when a company simply isn’t doing something at all, and the audit team discovers it. Let’s say there is a database that wasn’t encrypted but should be. Then, when the audit team points it out, the company turns on encryption. In that case, suddenly generating evidence won’t be sufficient at all, because the company should have been doing so for a significant period of time before the audit team arrived. The audit team would likely then also inquire about all the other related audit subjects that could come into play (encryption policy, possibly data classification policy, encryption procedure, etc.) and fail the company there as well.
An additional area of flexibility is simply achieving the next lowest level of compliance you need. For example, Maturity Level 1 (ML1) doesn’t really require, but strongly encourages, the use of administrative controls, such as policies, standards, and procedures. Most companies struggle with administrative controls because they lack experienced, certified security personnel to oversee them. In the case of ML1, a company can simply “demonstrate” security to achieve ML1 and not worry about the administrative controls. However, in this case, the company wouldn’t be allowed to have CUI data, as that would require ML3.
There are also new information classification acronyms that you need to understand. Don’t worry, it’s really only two…FCI and CUI.
FCI stands for Federal Contract Information. Essentially, this is simply the “awareness” of federal contract details. Now, before I go on, some contracts are classified in such a way that even knowing the contract exists, without any other details, would require a security clearance above the CMMC model. Think NSA, for example. Regardless, contracts that aren’t actually classified can still pose a risk to the US Government simply by being understood to contain unclassified contract details. For example, take any random military installation that places a one-time contract for banquet tables, a PA system, and food services for 500 people in six months. A simple Google search reveals that this random military installation is primarily focused on military intelligence. The odds would likely be very high that the persons attending would likely be involved in the intelligence community; thus, a hostile entity may want to have surveillance of who entered the base or find a way to get a person on the food service team that serves food at the event itself, or for any other reason involving surveillance. Another option would be to completely compromise the food service company and simply poison the food to eliminate the 500 participants. That was just an example revolving around a banquet, but also consider awareness of an ammunition order, or maybe a large order of Hellfire missiles, and then consider why the order might have been made. A large purchase of Hellfire missiles may indicate the start of a ground conflict somewhere using Apache helicopters. These are just some of the concerns related to FCI. The ability to handle FCI data requires at least a CMMC ML1.
CUI stands for Controlled Unclassified Information. Another way to put it, very simply, is anything that still needs to be protected from outside sources but doesn’t hold a federal classification level of at least SECRET. Essentially, this is contract-related information, but it is much more technical. Imagine a widget that a private company must build for a communications satellite. The specs for the widget would be CUI data, and because the company was building the widget under contract, they would also have FCI data.
Now, someone is probably thinking, "Why don’t they just push all CUI data up to the SECRET level?" Great question!! The answer is that the company would then be required to have what is known as a SCIF, which is essentially a very secure area that would be equivalent to what the DoD would have to protect SECRET material on an actual military installation….and would be very cost-prohibitive to companies in general. So much so that some companies simply wouldn’t be able to be involved in DoD business in any way. Larger companies could, but then lawsuits over monopolies would likely pop up, and smaller businesses, such as minority-, woman-, or veteran-owned businesses, probably wouldn't be able to participate. Protecting smaller businesses that are unable to participate would also affect the federal funds specifically set aside for small businesses. It’s important to understand that, to interact with CUI data, you must have at least ML3.
In the interest of reducing confusion and hassle for companies, let's also discuss audit responses that would be absolutely unacceptable when the audit team is present.
Accepting risk – Not an option at all. Just because a company chooses not to do something doesn't mean it should accept the risk; it simply won’t fly for CMMC. Either the company is doing what it should to achieve the CMMC minimum standards (and will pass), or it isn’t (and will fail). What this will eventually boil down to, in the opinion of the DoD, is that the life of a soldier will be at risk, and it would be intolerable to allow a 3rd party just to accept risk if a soldier's life is at stake. If your company hasn't implemented an Enterprise Risk Management program, Arrakis can help. Read our one-pager on ERM here.
Company culture - CMMC has specific, if not a little vague, wording that does indicate a culture that is compliant with CMMC. Honestly, CMMC could probably reinforce this a little better. The CMMC has specific language that requires the company to demonstrate habitual and persistent activities. This means the company must demonstrate to the audit team that administrative controls and security activities are deeply ingrained in its personnel.
Funding – In this case, the CMMC doesn’t mince words. A lack of funding to become CMMC compliant clearly shows a lack of leadership support, as funding comes from leadership. Again, CMMC requires compliance to be compliant, so if there is a requirement, even at the lowest level of ML1, that isn’t properly funded, then even ML1 won’t happen. Along those same lines, if there is a thousand-person company with only one infosec guy, the auditor is likely to wonder whether leadership has properly funded the infosec team. Additionally, if we had a 200-person organization (where having a single infosec guy might be more appropriate) with global locations, the audit team might wonder how a single person could perform 24/7 operations without sleeping. Essentially, the audit team is experienced enough to know what personnel and technology should be properly funded for a company of a particular size. There must be leadership buy-in at all levels to make this happen.
Experience and certifications – In some companies, it’s not uncommon to see someone who was spontaneously designated the Information Security Officer, the Data Privacy Officer, etc, without any experience or certifications in the new specialties suddenly thrust upon them. I call this person a sacrificial lamb, and I do not doubt that some of the readers are either chuckling because they have experienced it or suddenly cringing because they are still experiencing it. This is a no-go in the CMMC world. Control AT.2.057 specifically states “ensure that personnel are trained to carry out their assigned information security related duties and responsibilities.” This means a few things:
- You have to be able to prove that training occurred. One way to do that is to show that you sent someone to training, or that the person hired is already certified, which implies that training occurred (otherwise, there would be no certification). Contact Arrakis for CMMC-compliant training.
- Regardless of the previous item, this also means that the person must be able to demonstrate their job in a manner that appears to be natural to the auditors. Thus, throwing someone into the fire at the last minute would likely leave the auditors less than impressed. This also removes all those really good test takers with no hands-on experience (I'm sure some readers also know some of these guys as well).
- These activities also apply to technology that your company may have. So, assuming you had one information security person, that same person must demonstrate competency with the technologies used by the information security program. In other words, you can’t implement a new technology that the infosec guy barely understands and expect happy auditors.
- Finally, there is nothing that indicates you have to have employees perform all of these functions; you can outsource, but you will need to do your due diligence on the outsourced entities based on exactly what role they will be performing. For example, Arrakis Consulting could be the entity that helps implement and manage your administrative controls through our GRC platform. In that case, Arrakis Consulting wouldn’t have access to any CUI data and wouldn’t need to demonstrate ML3 maturity to the company. This would leave that entire section out of the lone-ranger infosec guy's responsibility. You can even bid on CUI-related contracts, but then subcontract the CUI work out to an ML3 subcontractor where the prime doesn’t even see the CUI. See our one-pager on GRC here.
There are a few gotchas as well. In other words, there are a few areas that will certainly bite you if you aren’t fully aware of them. Finding out the hard way can be very expensive for your company. See below:
- Administrative controls, such as policies or procedures, that conflict with what is actually being done. So, let’s say that your policies and procedures indicate that encryption must be used, how it must be used, and why it should be used. Still, it isn’t actually being used… that would definitely be a gotcha, as administrative controls are the foundation for any security or privacy program. The audit team would naturally conclude that you don’t actually do what you say you do, which would also lead them to believe that security activities were not habitual or persistent, or possibly being performed without leadership's awareness. To make it worse, once you open that can of worms, the audit team will naturally start to question everything else you are doing. The only caveat to this is ML1, where administrative controls aren’t even required; however, if there are administrative controls in ML1, they must not contradict demonstrated ML1 activities—one-pager on policies here.
- Not enough evidence can always get you. Saying you do something isn’t the same as being able to prove you’ve done something multiple times over the last few months without some sort of auditable system of record. The audit team is obligated under CMMC to obtain evidence using two of three methods: interviews, documentation, and testing. About the only possible loophole in this area, however, would be extremely risky and would require the auditor to agree to shoulder surf during control testing to see clearly that the person performing the activity showed no confusion on how to perform the task, in addition to interviewing enough people to believe that the activity has happened that way consistently. We advise against taking such a gamble.
- Assuming you will become certified in a very short timeframe is likely going to be a gotcha. Let’s assume you want to handle CUI data; that would require at least ML3. However, that means you would have to demonstrate “habitual and persistent” activities for all areas of ML3 and below. 130 controls involve all types of internal personnel. Is it really possible to achieve that level of maturity quickly? Likely not.
- Not fully implementing a specific required area, but having a plan to implement that required area is also a failure. At the time of the audit, you must be performing all required controls; otherwise, you won’t pass that area, which will lead to overall failure. Planning to do something doesn’t count as actually doing it. Also, having a dependency on a tool that the company doesn’t own is equally a failure.
- Not performing proper due diligence on your employees or your subordinate vendors. You will be expected to prove that this was done and that it aligns with your onboarding policy and procedure. Unfortunately, in today’s world, companies are not fully performing due diligence upon hire or internal assignment. To compound that issue, in some states (California), it is illegal to refuse to hire someone based on their criminal history… yet if you don’t consider that, you could violate CMMC. A possible loophole would be to simply not operate in California.
- Being under the assumption that you can apply a tool or some form of technology to solve a problem that a human can’t. While that sounds great, a human must manage the tool or technology, and the company must ensure the personnel assigned to perform the task understand the tools and techniques clearly, so they are trained and can withstand an auditor's interview.
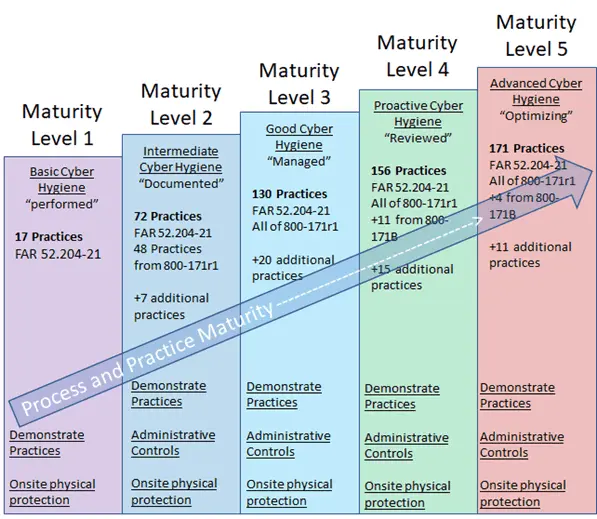
Now that we have gone through the above, let’s talk about maturity. CMMC is broken into 5 maturity levels, with requirements sourced from multiple sources. Sources such as FAR 52.204-21, NIST 800-171 (including subsets), and various additional requirements were added to supplement what the DoD felt was missing. Each maturity level has increasing requirements, where the next highest level requires you to fulfill the desired level and all lower levels.
Maturity level 1, as previously discussed, is the lowest and easiest to comply with, as the company only has to demonstrate activity that meets the requirements, without having to provide administrative controls such as policies or procedures… which are still strongly recommended, though. There are 17 practices found in ML1, all of which are pulled from FAR 52.204-21. FYI, a practice is something that is being done but may not be fully documented or mature.
Maturity level 2 is where it starts getting more intense for the company seeking certification. We jumped from 17 practices to 72 and picked up most of them from NIST 800-171. At this stage, ML2 requires documented policies and procedures, and the company must demonstrate habitual and persistent activity. Ad-hoc activities aren’t permitted, and any activity performed must be auditable. Thus, if you don’t have an auditable system of record for activities that are being performed, then you should get one.
Maturity level 3 again increases the difficulty almost two-fold by requiring 130 practices, with all practices from NIST 800-171 in play and an additional 20 practices that indicate good cyber hygiene on the part of the company.
Amazingly, ML4 has only 156 practices (currently), whereas ML3 and ML5 have 171 each. Why did we group those and emphasize “currently”? Well, it’s because the CMMC hasn’t fully fleshed out ML4 and 5, and both could change.
One thing to point out: regardless of maturity level, all physical security controls require an on-site visit by the audit team, and all are contained in ML1. This is unavoidable.
The Audit Process is pretty similar to an ISO or SOC2 audit, in that independent teams perform functions to reduce the risk of conflicts of interest.
To increase the chances of success, the company seeking certification is advised to contract with an experienced 3rd party to help them prepare for the audit (such as Arrakis Consulting). This is called pre-assessment readiness and can save a lot of time and money while reducing stress during the actual audit. Ideally, at this point, we really don’t even want CMMC to know we are seeking certification, as we really don’t know how long it will take the company to become compliant enough to pass a certification audit.
Once the company is ready, it reaches out to a C3PAO (an independent company that can perform audits on behalf of CMMC) and verifies that it is in good standing with CMMC. If not in good standing, then another C3PAO is required.
After a contract is signed with the C3PAO, the C3PAO requests an assessment ID from the CMMC for that company's assessment. Then the C3PAO assigns an audit team composed of people certified to perform an audit at that maturity level. For example, an auditor certified only for ML1 can’t do ML3, but an auditor certified for ML3 can do ML1-3. This audit team performs the audit, generates a report, and sends it to the C3PAO for QA review. Assuming no discrepancies, the C3PAO submits the report, the assessment ID, the audit team IDs, and a certification recommendation of either pass or fail. If the recommendation is a “fail,” CMMC does not perform any further review; however, the company can file a dispute to seek an alternate outcome. Assuming a recommendation of “pass,” the CMMC conducts another QA review and, if it agrees, issues a certification to the company. After certification, the CMMC updates the corresponding database to indicate that the company has met a specific maturity level.
There are also various areas to prevent conflicts of interest. For example, the team that prepared the company for the audit can’t participate in the audit itself. The audit team can’t provide advice or guidance during the audit. If the C3PAO is also a company that helps client companies get ready for an audit, then the entire company can’t be involved in the actual audit. So, from a business standpoint, the C3PAO really needs to determine if they want to be in the helping business or the audit business on a case-by-case basis.
What should also be understood is who exactly gets interviewed as part of the audit. The person actually performing the activity will be audited. No more will a manager represent someone in an audit to indicate what the employee is doing… now, the audit team will interview the employee themselves in a private setting. While it could be considered that the employee is concerned about reprisals for telling the truth, it should also be understood that the audit team wants to hear the relevant information straight from the person who performs the activity.
What can go wrong should also be considered. We already discussed the conflict of interest and the possibility there, but other areas could pose issues as well. First, the company should never allow evidence containing CUI to leave its premises, nor should an audit team request CUI evidence. Doing so for both defeats the purpose of CMMC and should be reported as soon as possible.
However, there are other areas the company should seriously consider in relation to possible sanctions. Any auditor can tell you that at some point in their career, a company has asked the auditor to look the other way. That simply can’t happen and exposes the company and its auditor to legal sanctions. Any auditor can also tell you that there is always going to be some company that is “less than truthful” about some evidence, or possibly telling either a prime contractor or the DoD itself that the company's security posture was something other than what it really was. This is called a violation of the False Claims Act, which essentially means any entity/person that makes a false claim in relation to a government contract can face hefty financial penalties, in addition to possible criminal charges. To make the point, the Department of Justice received more than $3B in settlements in 2019 alone because of this. So how did the DoJ find out? Well, whistleblowers get between 15% and 30% for reporting false claims. When you think of how many millions some contracts are worth, even 15% is an instant retirement. Cisco was fined $8.6M, of which $1.3M is a whistleblower award. A video related to the False Claims Act is further down this page.
Not to forget, there is also the “Christian Doctrine,” which essentially states that any entity that signs a government-related contract must protect information (such as FCI or CUI), regardless of whether it was actually written into the contract. Essentially, just because you don’t know, or it’s not spelled out in the contract, doesn’t mean you can avoid what you should be doing…even if you didn’t know you should be doing it. FYI, this is pretty much across all government contracts.
There is also the prime/subcontractor relationship to consider, as every upstream company is obligated to ensure that any downstream company is compliant with the appropriate CMMC maturity level to collaborate on DoD contracts. The liability for a company failing to perform appropriate due diligence on downstream companies can be substantial and fall under both the False Claims Act and the Christian Doctrine.
Prediction – Arrakis Consulting predicts that all federal contracts will soon include some form of CMMC language or requirement once CMMC is fully enforced (this has now been set for Nov. 10, 2025). This prediction is simply because there are too many interconnections between companies that eventually lead to government contracts. Additionally, NARA is the government body that defines what CUI means...and it is vast...so much that it is clearly far beyond just the scope of the DoD. Arrakis Consulting also predicts that highly sensitive state and local government contracts are likely to have the same effect. Specifically, contracts involving state entities such as revenue and taxation, prisons, health, etc.
Now for a pick-me-up bit of good news. 2028 is when the CMMC will be fully implemented across all DoD contracts. Start getting ready if you haven’t already.
Arrakis can help you become more compliant or remain compliant by offering an unbiased 3rd-party assessment tailored to the framework or regulation you are required to conform to, as well as helping reduce your overall risk. See our one-pager on Internal Audit here.
Additionally, Arrakis can provide regulatory or compliance training to your company to help better prepare you for a regulatory environment. Click here to see just some of our options to train you in regulatory compliance.
These solutions can be in several forms:
3rd-party audits and assessments - All major frameworks require a 3rd-party assessment of vulnerability and risk, or a 3rd-party audit of your information systems. Arrakis can be your trusted advisor, providing an unbiased, honest assessment of where you feel weak or where a regulatory agency may target you. Don't be caught short in high-risk compliance areas like GDPR, FFIEC, FISMA, PCI, HIPAA, etc. See our one-pager on Internal Audit here.
Business Impact Analysis (BIA) - As a matter of good practice, a BIA should be done at least yearly to ensure that you completely understand the level of impact to your business should any portion of your business process fail. How long can you stay down without a major incident? How long can you stay down before your customers decide to move to another solutions provider? Knowing the impact, both qualitative and quantitative, on your business is vital. Arrakis can help you realize exactly what your impact is. See our one-pager on BIA here and Disaster Recovery / Business Continuity here.
Gap Analysis - regardless of the framework you are required to follow, there is always something that needs to be reviewed to identify your gaps or weaknesses, so you have targeted, actionable items to focus your remediation or improvement efforts. Don't be caught short in high-risk compliance areas like GDPR, FFIEC, FISMA, NIST, HIPAA, PCI, etc. See our one-pager on Internal Audit here.
Framework implementation, consultation, or support: All companies that process regulated data must comply with a security framework. Whether it be NIST 800-53, NIST 800.171, PCI, ISO 27001, FFIEC, etc., we can help implement or provide consultation services to make your current implementation easier. Additionally, in several situations, companies must comply with multiple frameworks or create a hybrid framework to reduce regulatory risk for the company and its executives. Arrakis can help guide you from confusion to a clear outcome.
Managed Services - Arrakis offers a suite of managed services and managed security services designed to help you become regulatory-compliant faster and take some of the effort and burden off your shoulders. This means that Arrakis can take on some of the responsibility for meeting compliance-related requirements. Still, it does not mean that Arrakis will take on accountability for ensuring your company's compliance. Unfortunately, from an accountability perspective, the company required to be compliant is the only entity that can be held accountable for compliance, and support companies should not be confused with it. Managed services are all "best effort", and there is no promise or assurance of being 100% compliant with 0% risk. It's impossible to reduce risk to 0%.
vCISO/CISO as a service - Some companies simply do not have the budget, experience, or training to have a CISO or an information security department. While all frameworks require a security department and a CISO, it simply isn't in the budget, or there isn't enough technical work to justify hiring the appropriate personnel. Arrakis can help you act as a trusted advisor to the CIO or COO at your company and, in effect, perform CISO functions. Technically, according to the frameworks, someone in the company still must hold the title of CISO; however, none of the frameworks indicate that the actual "work" cannot be outsourced to a reputable 3rd party. Don't be caught short in high-risk compliance areas like GDPR, FFIEC, FISMA, etc. See our Business Services page for more information.
vCIO/CIO as a service - Similar to the CISO as a service bullet item, some companies are more focused on building their business and increasing their profit margin, and just don't have the time or experience to perform CIO functions. They have a strategy, but cannot execute. Arrakis can help be the IT glue that binds all the technological functions into a cohesive package to fill this gap. The professionals at Arrakis have, on average, over 20 years of experience in all aspects of IT, including managerial functions such as budgeting, project management, and process improvement. See our Business Services page for more information.
Governance, Risk, and Compliance - Regardless of what framework your company is required to follow or the level of maturity, all companies bear some risk because they are in business. Our GRC team can help your company stay in compliance with regulations, assess and track risks, and provide an easy-to-follow governance model to ensure your company operates in a stable manner that keeps auditors happy. Don't be caught short in high-risk compliance areas like GDPR, FFIEC, FISMA, etc. See our one-pager on GRC here.
Policy Creation and Review - Quite often, companies have some form of policies in place. Still, most of the time, those policies do not meet auditors' requirements or the company's frameworks. While the company intends to be compliant, the deficient policies do not help and only draw closer the attention of auditors. Arrakis has years of experience writing policy and can help bring you up to speed on the frameworks and improve your success rate when it is time to be audited. See our one-pager on Policies here or subscribe directly to our Policy Forge platform.
Need extra help? Subscribe to our online practice test engine. Hundreds of questions are designed to be more difficult than the actual test to increase chances of success.
Subscribe here and gain access to all our practice tests.






Arrakis Consulting © 2017-present
DUNS# 081000330
CAGE Code 80N01
A Service-Disabled Veteran-Owned Small Business (SDVOSB)
© 2017 - Present, All Rights Reserved
Book an Appt. Online
- Arizona (602)-383-4141
- Texas 713-364-9870
- California (650) 540-7676
- Montana (406) 220-5797
- Washington (206) 472-7910
- Utah (385) 284-8977
WhatsApp - (602) 383-4141
SMS - (602) 383-4141
FAX 505-806-7630
Email: sales(@)arrakisconsulting.com
Legal: legal(@)arrakisconsulting.com
Accounts Payable: ap(@)arrakisconsulting.com
Our mailing address is found in the Contact Us form

